

Dev tools detection
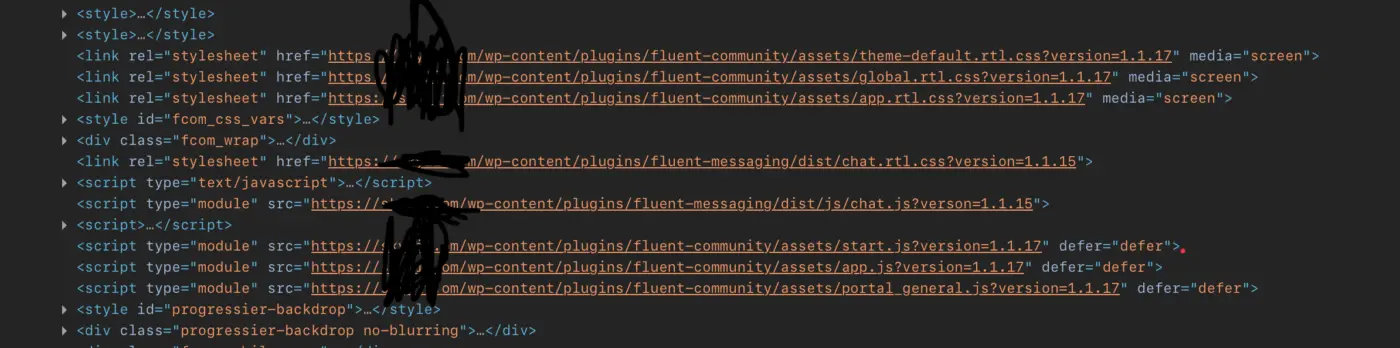
Is there any way to hide information in my web from detection dev tools?

Why you wanna do that?
Shahjahan Jewel For security, it is better to encrypt the paths and scripts
You can't hide this HTML source code (make it completly invisible) in a browser because your browser needs HTML code to render/run and view your web page.
view-source:YourDomain.comNote: There are some other methods to minimize web scraping or code copy pasting (server side rendering, encapsulate your source code with React JS) but I don't think this is what you are asking for.
Ps. You can change your plugins folder name (or a /plugin path) but in a long run this is just a wasting of time - check #InspectWP #WPScan #WP-JSON
Ps2. Sooner or later probably AI Agents will be able to detect everything what you try to hide (especially if it's not a custom made but out of the box solution).
Big companies like: CNN, Reuters, NASA, White House, the Gov of Sweden and Finland dont feel the need to hide their sites that are on WordPress.
There's absolutely no need for you to do so either.
Note: Big Companies create their own solutions and plugins for their WordPress websites but I dont think it's our case so we trust external companies (Plugins Developer) who can get in to our WordPress if they want #InDevelopersWeTrust
When it comes to STO:
What does “Security through obscurity” (STO) mean?
STO is based primarily on hiding important information and enforcing secrecy as the main security technique. By using security by obscurity, some people think they are going to minimize the risk of getting targeted by an attack.Here are 2 real-life examples:
- Hiding the key to your front door under a nearby rock or the welcome mat. The principle is simple: your house will be “secure” until a thief discovers the key in its hiding place. That’s when your house becomes vulnerable.
- The same goes for building your house in the middle of the forest. Being surrounded by trees and shrubs, it’s “secure” within that forest. However, as soon as someone walks in and discovers your house, it’s vulnerable.
This is similar for WordPress. Let’s say that you want to make it more difficult to find out that you’re running WordPress and also want to hide a few other things. All of these are supposed to make you more secure. But none of them is near as valuable as making sure that you lock the metaphorical door.
If you rely solely on STO to replace real WordPress security, all is lost as soon as its secrets are revealed.Now, back to this case.
Hackers/bots can and will attempt to exploit your plugins and themes regardless of whether they know what you have installed. They’ll just try it, and if they get a hit, they’ll keep at it. Hiding the “names” of what’s there won't prevent that.
What will prevent trouble is ensuring all your plugins and themes are kept up to date
Ps. Encrypting paths and files could slow down the website. Paths in this case also needed to be randomized for each visitor session but it wouldnt give any additional benefits for open source WordPress.