FluentAuth 2FA login screen a security concern?
Hi, I ran into the "Cannot complete this step?" message today after entering my username and password, and I wanted to ask about the way the bypass constant is displayed. The message shows:
define('FLUENT_AUTH_DISABLE_TWO_FA', 'my-random-token-here');
directly on the login page, before the second factor has been verified. My question is. Since this value is unique per account and effectively acts as a secondary secret, is it safe to expose it in plain text on that screen?
Just wanted to raise this since it wasn't obvious to me at first that the string was a secret rather than just an example.
Thanks again for the great plugin.
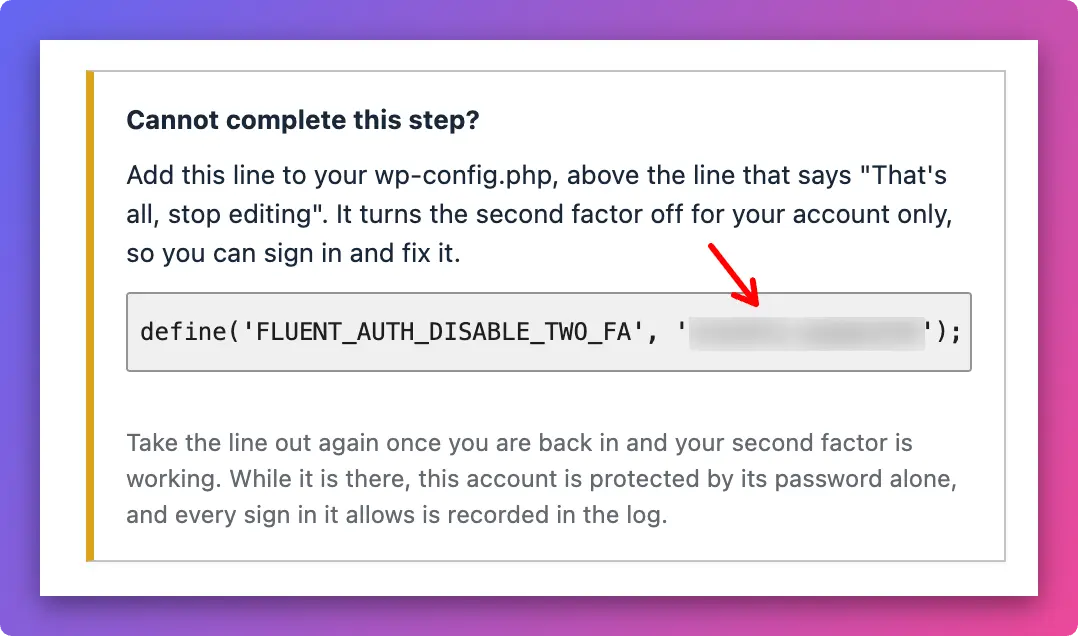
After checking, the value hidden above is exactly my WordPress username (user_login), not a random token.
Ben Berghout That screen only shows who the administrator is from the login. Since you already verified with your username and password, it shows the message in case you lose your device factor (Passkey / TOTP).
Nice update, this is better! It also prevents someone from looking over your shoulder.