

Bunny Stream Integration
Hi Jewel,
We recently moved to FluentPlayer (LTD, 100 sites) across our client sites, and I spent some time in the Bunny Stream integration code. Two findings I think are worth your attention.
1. The account API key is a blocker for agencies
The Bunny Stream integration requires the Bunny account API key. That key grants access to every video library on the account. On an agency setup, this means each client site we configure technically holds access to every other client's videos. One compromised site or one shared admin login, and the whole portfolio is exposed.
What makes this frustrating is that your code already works the right way. Every actual operation in BunnyCDNService and BunnyCDNStreamIntegration takes a library-specific $libraryApiKey, resolved through getLibraryApiKey() from settings['libraries']: getVideos, getVideo, createVideo, updateVideo, deleteVideo, uploadVideo, getCollections. The account key is only used in two places:
- getLibraries() hitting GET api.bunny.net/videolibrary, to discover libraries and populate settings['libraries']
- fetchPullZone() hitting GET api.bunny.net/pullzone/{id}, to store Hostname and SecurityKey
Both are convenience only. Bunny already exposes per-library API keys, so the scoping exists on their side.
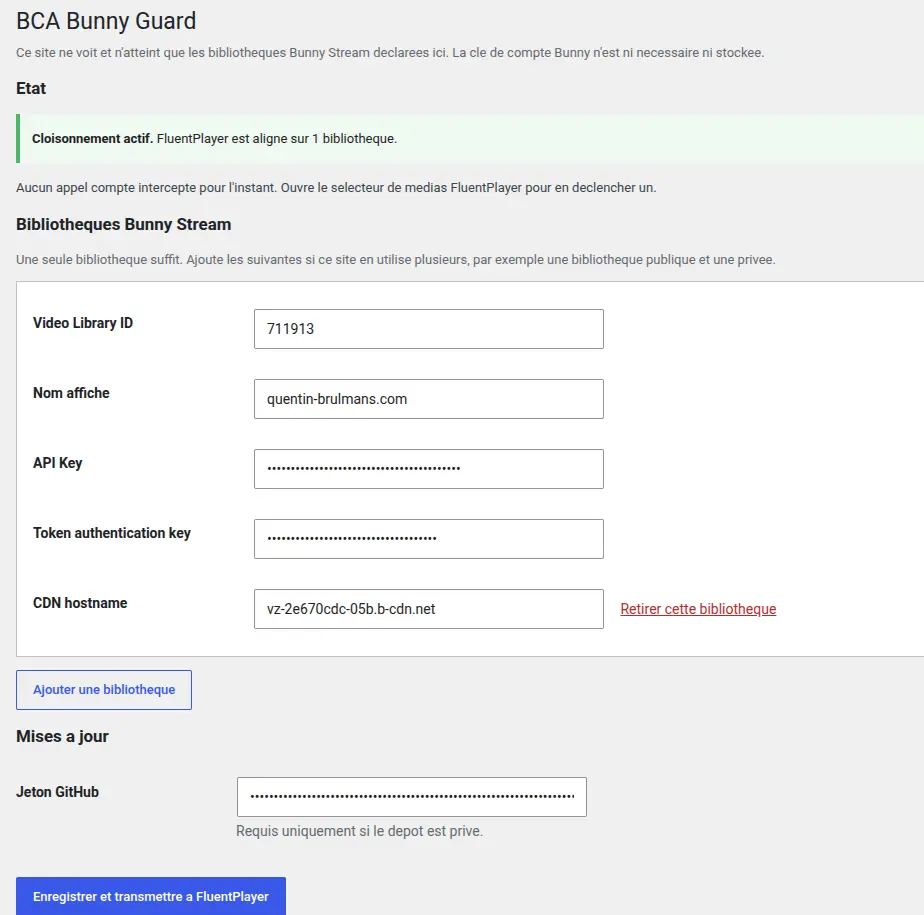
What I would suggest: a "manual library" option in the Bunny Stream settings, letting the user enter Library ID, library API key, pull zone hostname and token authentication key directly, and skipping the discovery call. Everything downstream keeps working unchanged. For agencies this turns an unusable integration into a safe one.
One related detail: updateLibrarySettings() resets settings['libraries'] on every discovery call, so any manual entry gets wiped whenever the settings are refreshed. Worth keeping in mind for the implementation.
2. CDN token authentication for Stream
Separately, I could not find CDN request signing for Bunny Stream. generateSignedUrl() and signBunnyStorageUrls() read cdn_security_key from the Storage integration, and generatePlayerToken() is documented for DRM license endpoints. In practice, enabling token authentication or referer blocking on a Stream library breaks playback, so both have to stay off.
That means Stream videos are reachable by anyone holding the direct URL. For clients selling courses through LearnDash or SureCart, that is a genuine concern. Is CDN token signing for Stream on the roadmap, or am I missing an existing setting?
I built a small add-on covering the first point on our own sites, so I know the approach holds. But it belongs in the core integration rather than in a workaround, and I would much rather use yours.
Attached is the settings screen from the add-on, just to show how few inputs this actually needs: Library ID, library API key, token authentication key and CDN hostname. The interface language is French, but the field labels tell the whole story. Happy to share the code or walk through any of this.
Kind regards,
Eric Brulmans
Shahjahan Jewel for you my friend ! ;-)

Yes, I have notified the team, They will improve the API integration. Thanks
Starting to use bunny a lot these days for streaming and video storage. Amazing value with a lot of tools. The bunny plugin is good, but this new player will make things SO much easier for users.